When the Wallet and the Chain Share the Same Ledger Kernel: Light Verification Nodes, Isomorphic Storage, and Sovereign Encrypted Reconciliation
In our earlier essays—Building Passkeys Into the Wallet Architecture and Why Your Wallet Should Audit Its Own Books—we posed a blunt question: If a wallet goes to extraordinary lengths to protect private keys inside a hardware secure enclave, yet blindly trusts whatever balance and transaction history a remote RPC server returns, is that wallet actually secure?
For years, the blockchain industry has lived with a strange architectural contradiction. On the server side, protocol engineers build intricate hash chains, Merkle trees, and Byzantine fault-tolerant consensus under the banner of "Don't Trust, Verify." Yet the moment data crosses the gateway into a user's mobile or desktop wallet, cryptographic verification vanishes. Most mainstream wallets degenerate into passive displays ("dumb clients") that render whatever JSON an RPC endpoint sends back, stashing local state into ordinary SQLite cache tables with no signatures, no hash chains, and no protection against cache poisoning or stale snapshots.
In the previous article of this series, Embedded Like SQLite, Verifiable Like a Blockchain, we showed how we extracted a lightweight, zero-external-consensus Verifiable Ledger Core and embedded it inside every ARC instance. Today, we follow that exact same kernel into the client endpoint to examine two foundational designs in ArcBlock's next-generation wallet architecture:
- The Wallet as a Scoped Light Verification Node: How every human wallet and every AI agent wallet actively audits its own account state;
- An Isomorphic Local Verifiable Ledger and Sovereign Encrypted Annotation Ledger (
ocap.annotation.v1): Why internal wallet storage should share the exact same cryptographic ledger kernel as the blockchain itself.
1. Generalized Wallets as Light Verification Nodes: A Million Endpoints, A Million Auditors
Traditionally, a "wallet" meant a mobile app or browser extension operated by a human. In an era where humans and autonomous AI agents collaborate side by side, our definition expands to the Generalized Wallet:
- Mobile DID Wallets and desktop/web wallets in the hands of human users;
- Every autonomous AI agent that holds its own DID, manages a budget, and signs transactions;
- Every backend application service (ARC instance) and IoT device that settles transactions or issues credentials programmatically.
Any entity that holds cryptographic keys and initiates transactions is a generalized wallet—and in our architecture, every generalized wallet is natively a Light Verification Node.
1. Why Verifying "Transaction Bytes Are in the Tree" Is Not Enough
From Section 8 of the Bitcoin whitepaper (Simplified Payment Verification) and Zcash compact block filters to Ethereum's eth_getProof and RFC 9162 Certificate Transparency logs, applied cryptography has long proven that a client does not need hundreds of gigabytes of full-node history to verify inclusion. A compact Merkle inclusion path against a signed root hash suffices.
In production engineering, however, naively porting classic SPV inclusion proofs into a modern ledger exposes two dangerous blind spots:
- Ledger Inclusion ≠ Execution Success: In a layered ledger that separates ordering from state execution, a transaction with a valid signature and sequence number is recorded in the ledger first; if execution later fails due to insufficient balance or guard conditions, it persists as
PERSISTED_FAILED(charging only the execution fee). IfentryHashonly commits to the raw request bytes (txRaw), a malicious or compromised gateway could hand a wallet a valid Merkle inclusion proof for a failed transfer and trick the UI into displaying "Payment Received." - Single-Transaction Inclusion ≠ Current Account Balance: Even if an incoming transfer genuinely succeeded yesterday, an inclusion proof for that single transaction cannot tell the wallet whether a subsequent outgoing transfer drained the account five minutes ago, or whether the gateway is serving a stale snapshot.
To close both loopholes, we hardened the entry commitment and checkpoint structure inside Verifiable Ledger Core (with chain-side proof endpoints and multi-source cross-checking advancing through continuous integration):
- Deterministic Receipt and State Commitment Binding: When every transaction finishes deterministic execution and invokes
finalizeEntry, itsentryHashcommits not only tosequenceandtxRaw, but also to a storage-engine-agnostic deterministic execution receipt digest (stateCommitHash, byte-for-byte identical across SQLite and Dolt). That commitment explicitly binds the execution outcome (OKvs.PERSISTED_FAILED), actual fee consumed, and post-transaction account balance andnoncesnapshot. - Trust Anchor and Checkpoint Quorum Verification: When the wallet invokes its local pure verification function (taking just
0.03ms–0.08msper proof), it first verifies the proposer signature and independent witnessQuorumCertificateon theCheckpoint, confirming thattxRootand the deterministicstateRootcarry valid quorum commitments at a monotonically increasing height. Only then does it verify that the target transaction's Merkle path resolves totxRoot. Altering a single digit of a balance or disguising a failed transaction as successful causes an immediate hash mismatch.
2. Local Pre-Computation, Double Confirm, and Dispute Settlement
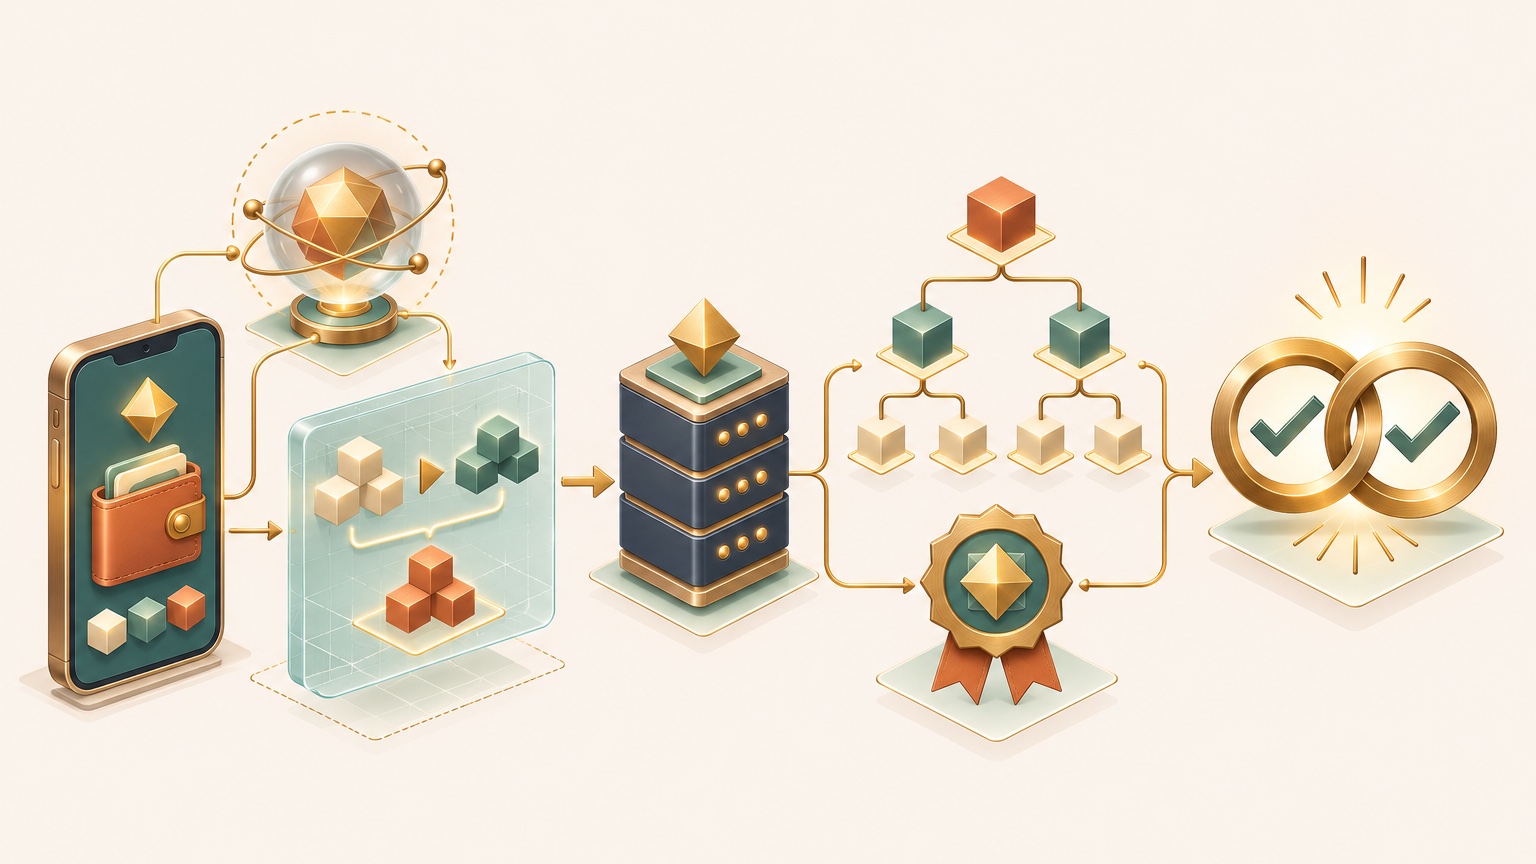
Beyond passively verifying proofs returned by the network, a Light Verification Node flips the transaction workflow on its head: before sending a transaction to the network, the wallet computes the expected outcome locally.
[1. Local Pre-Computation]
  Based on its locally verified account state and deterministic rules,
  the wallet computes a Reference (expectedBalance, expectedNonce, baseCheckpointHash)
        │
        ▼
[2. Submit Transaction + Reference] ──► Node executes deterministic transition & compares
        │
        ├─► Case A: Node-computed state matches the wallet's Reference byte-for-byte
        │     └─► ✅ Double Confirm (independent calculation match — highest confidence)
        │
        └─► Case B: State divergence (e.g., a concurrent incoming transfer or auto-debit landed first)
              └─► Node returns the intervening ledger entries + Merkle inclusion proofs
                    ├─► Wallet replays & verifies the delta ──► Sends ACK to advance baseline
                    └─► Proof or state fails to close ──► Triggers alert & Settle flow, switches gateway
Think of it like reconciling a bank deposit or credit card statement. If you know your balance should be $1,000 after a deposit, and the teller's screen says $999, you don't just nod blindly—you ask for the intervening ledger entries. If there is a valid $1 automated fee backed by a receipt you previously authorized, you verify it and advance your baseline. If the teller cannot produce a valid signed entry or the math still doesn't add up, you reject the statement immediately and open a dispute (Settle).
In a conventional blockchain, security depends solely on whether a few dozen or a few hundred server nodes remain honest. When every wallet is a light verification node, an application with 100,000 human users and 10,000 autonomous AI agents is surrounded by 110,000 online, independent auditors at the edge. Any gateway that attempts to serve tampered state is caught within milliseconds by thousands of endpoints simultaneously.
2. Why Internal Wallet Storage Must Be an Isomorphic Verifiable Ledger
Once a wallet stops blindly trusting remote RPC servers, a second uncomfortable question arises: Can the wallet even trust the local database sitting in its own flash storage?
Consider how much critical state a modern identity and asset wallet manages locally every day:
- Multiple derived or imported accounts, Passkey hardware credential bindings, and monotonic signature counters (
signCount); - Dozens of Verifiable Credentials (identity attestations, memberships, developer certificates, access passes) across issuance, update, and revocation lifecycles;
- Session grants and spending limits delegated to web apps, DApps, and AI agents;
- Cross-device encrypted backups, cloud restores, and historical baselines migrated from earlier wallet generations.
In conventional wallet engineering, this state is scattered across ad-hoc SQLite tables and key-value caches. If the app crashes mid-write, a cloud sync drops a batch, or an object-storage backup is rolled back to a two-week-old snapshot, the UI silently renders stale permissions or missing credentials without knowing anything went wrong.
Our solution is architectural: instead of maintaining a patchwork of ad-hoc cache tables, we embedded @arcblock/ledger-core directly inside the wallet (with byte-compatible TypeScript and native iOS Swift ArcWalletLedger implementations), turning internal wallet storage into a 100% isomorphic Verifiable Identity Mini-Ledger.
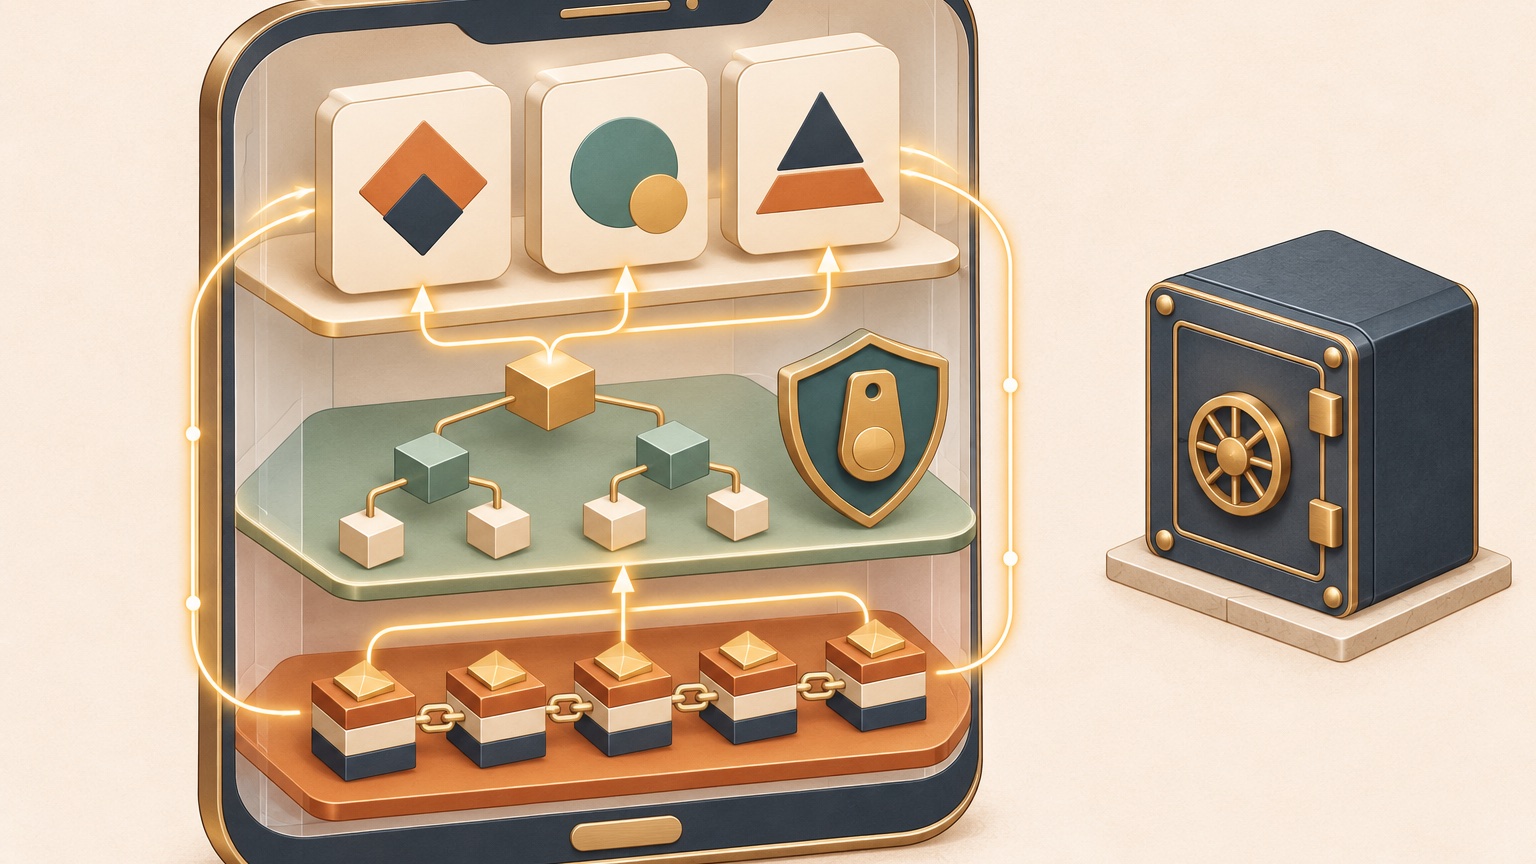
1. Three-Table Isomorphic Architecture: Append-Only Events, Signed Checkpoints, and 100% Rebuildable Projections
Inside the wallet's local SQLite database, all core state converges into three strict layers mirroring our chain-side three-database separation:
| Local Storage Layer | Table / Component | Responsibility & Cryptographic Invariant |
|---|---|---|
| 1. Single Source of Truth (Append-Only Event Log) | arc_wallet_events | Every state change (GENESIS_MIGRATION_IMPORT, PENDING_CLAIM_ADDED, CREDENTIAL_CLAIMED, CREDENTIAL_REVOKED, PROPOSER_ROTATED) is appended as an immutable event linked via deterministic computeEntryHash. |
| 2. Sealed Commitments (Signed Checkpoints) | arc_wallet_checkpoints | Bridges IncrementalMerkleTree and computeCheckpointHash, sealing event windows with the account proposer's cryptographic signature. |
| 3. Derived Read Views (Deterministic AFS Projections) | arc_wallet_projections + WalletLedgerAFSProvider | Exposes standardized /wallet/* read projections and controlled actions to the UI. The UI layer never queries raw underlying tables directly. |
This isomorphism transforms client-side reliability:
- Corrupted Cache? Wipe and 100% Deterministically Rebuild (
wipeProjectionCache+rebuildProjections): Becausearc_wallet_projectionsis a pure function ofarc_wallet_events, if a sudden power loss corrupts the projection cache—or a wallet update introduces new view columns—a single command wipes the projection table and replays the local event log from genesis, restoring every credential lifecycle state (including distinguishing history-preserving"revoked"records from permanently erased"tombstoned"records). - Crash Self-Healing and Fail-Closed Verification: On every cold start,
audit, or cloudrecoverAndHeal, the wallet requires a pinnedtrustedProposerPublicKeyHexand verifies the entire hash chain, Merkle inclusion proofs, and PasskeysignCountmonotonicity (preventing cloned authenticator replay). If the trust anchor is missing or a single hash mismatches, the ledger fails closed with a deterministic error code rather than rendering unverified state.
2. Four-Category Data Ownership Classification and the "Zero Secret Material in Ledger" Rule
The most dangerous trap when building a verifiable wallet ledger is confusing verifiability with confidentiality—or worse, accidentally logging private keys or seed phrases into an append-only event stream.
To make that impossible by construction, the wallet ledger kernel enforces a 4-Category Data Ownership Classification backed by runtime guards:
- Public / Structured Lifecycle Events: Account creation, key rotation, credential status transitions, and session grants—recorded structurally as part of the hash chain;
- Sensitive Private VC Claims: Personal identifiers or private attributes—encrypted prior to append using AES-256-GCM envelope encryption (
encryptPrivateClaims, binding the wallet ID and credential ID as Additional Authenticated Data) so the ledger stores only ciphertext and integrity commitments; - Rebuildable Projections & Settings: Ephemeral indexes and UI preferences that can be discarded and regenerated at any time;
- Hardware Keyring / Secret Material: Private keys, seeds, and recovery phrases reside exclusively inside OS hardware security modules (iOS Keychain / Secure Enclave). Built-in
assertNoSecretMaterialInProjectionguards inspect every payload and reject raw keys or mnemonic patterns before a single byte can enter an event, projection, or cloud backup.
3. Completing the Reconciliation Puzzle: The Sovereign Off-Chain Encrypted Annotation Ledger (ocap.annotation.v1)
Even when a wallet verifies on-chain cryptographic proofs and maintains an isomorphic local mini-ledger, real-world financial reconciliation still hits one everyday frustration:
An on-chain ledger records cold hashes, DID addresses, and token amounts—not human business context.
Think about opening your wallet or block explorer to review last month's activity:
- You see a
TransferV3transaction consolidating small balances from four addresses into a fifth, and three weeks later you cannot remember which sub-accounts those four addresses belonged to or why you consolidated them; - You see a payment to
did:abt:z1..., with no reminder of which merchant or invoice SKU it settled; - A partner sends you an expense reimbursement and wants to attach a private memo—putting it on-chain exposes your business relationship to the world, while storing it in a centralized web database means losing it the moment you switch apps or the server shuts down.
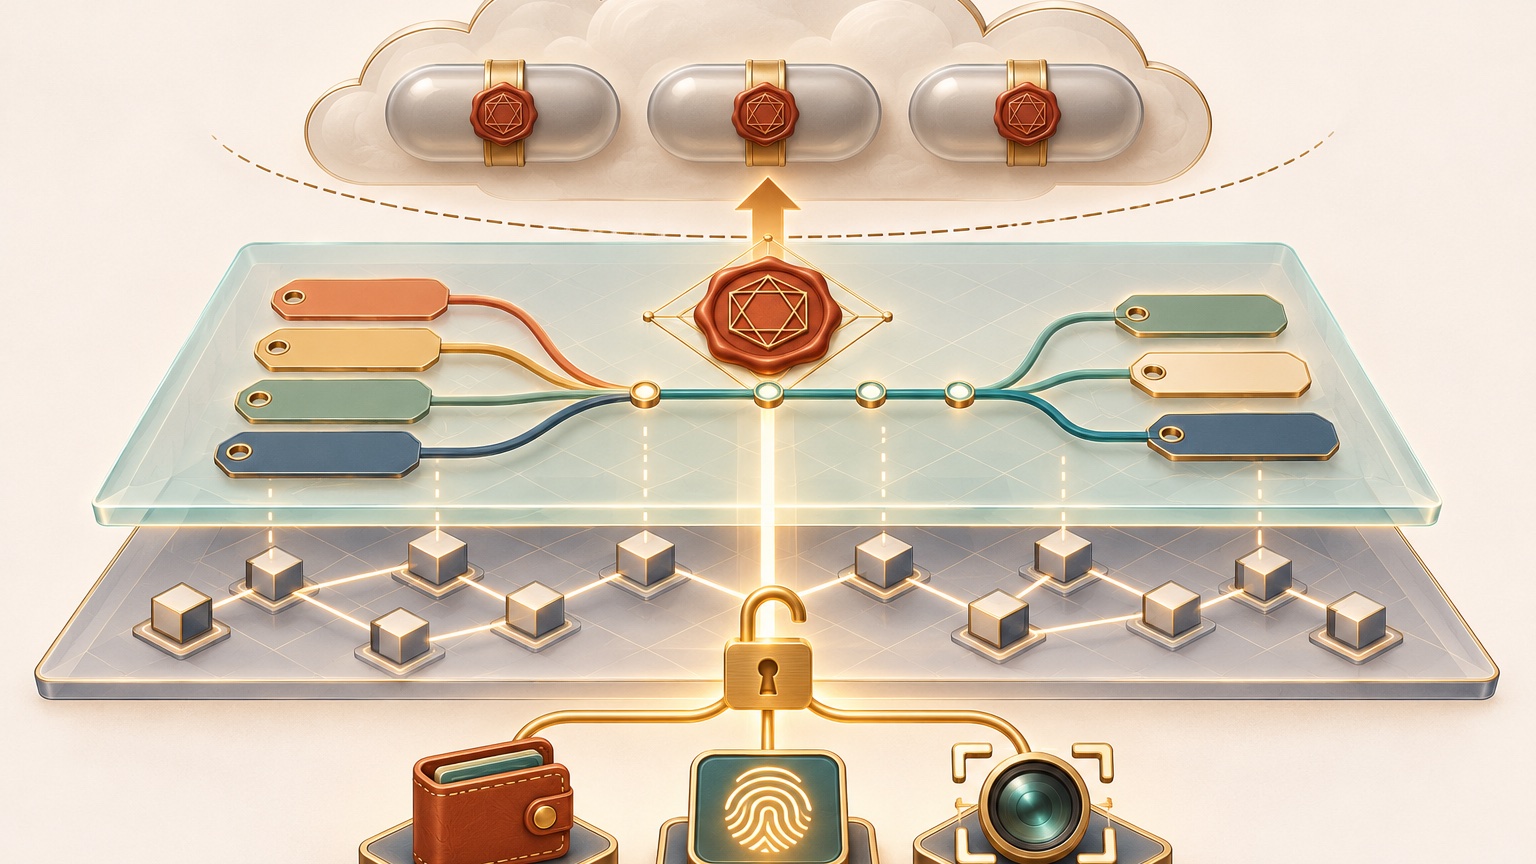
To solve this permanently, we designed and built the Sovereign Off-Chain Encrypted Annotation & Reconciliation Ledger (ocap.annotation.v1) inside @ocap/ledger-core. It runs on the exact same EmbeddedLedger (VLedger) kernel, purpose-built for zero-knowledge cloud synchronization and cross-device private reconciliation.
1. Zero-Knowledge HMAC Blind Indexing and Anti-Poisoning Binding
A user's annotation ledger syncs across mobile wallets, desktop browsers, and block explorers through their personal sovereign storage (ArcSpace / DID Space)—yet the storage server must never learn which transaction or address the user is labeling.
Accordingly, target identifiers—whether an account did:abt:..., a transaction hash txHash, or a specific multi-input/output leg <txHash>#in:0 / <txHash>#out:1—never appear in plaintext in indexes or cloud storage:
blindTargetId = HMAC-SHA256(K_idx, lenPrefixed(chainId, targetType, normalizedTargetId))- Cloud storage sees only a pseudorandom
blindTargetIdand an AEAD-encrypted ciphertext payload; it cannot even tell whether an annotation refers to an account address or a transaction leg. - Anti-Poisoning Ciphertext Binding: Whenever the client decrypts an annotation payload using
K_enc, the kernel recomputes the HMAC from the decrypted inner(chainId, targetType, targetId)and verifies that it matches the outer signedblindTargetIdbyte-for-byte. Any attempt to swap ciphertext labels between a phishing address and a legitimate counterparty is rejected immediately upon decryption. - Because the annotation history itself is an append-only
EmbeddedLedgerwith signed Merkle checkpoints (supporting incrementalbackupToArcSpaceandsyncFromArcSpace), the cloud provider can neither read your notes nor silently drop or alter a single historical memo.
2. Tri-Modal Cross-Device Key Derivation and Four Core Reconciliation Workflows
To let users unlock their private reconciliation book seamlessly across mobile wallets, desktop browsers, and the Chain Explorer, ocap.annotation.v1 supports three cryptographic key derivation and grant modes:
- Native Wallet Master Derivation (
WALLET_SECRET): UsesHKDF-SHA256with domain separation to derive three independent subkeys:K_idxfor blind indexing,K_encfor AEAD payload encryption, andK_sealfor anti-phishing visual seals; - Hardware Passkey Direct Unlock (
PASSKEY_PRF): Leverages the WebAuthn PasskeyPRF(pseudorandom function) extension so a user can touch their fingerprint sensor in the browser and derive the unlock keys directly in local memory without exporting a single private key; - Scoped QR Session Grant (
WALLET_QR_SESSION_GRANT): When inspecting transactions on a workstation block explorer, scanning a QR code with DID Wallet signs an ephemeral session grant bound strictly toviewerOrigin,sessionId, and an expiration timestamp—instantly overlaying your private labels onto raw on-chain addresses in browser memory.
Built on this foundation, four everyday reconciliation workflows converge into one verifiable ledger:
- Address & Sub-Account Identity Graph: Label primary accounts,
SELF_SUB_ACCOUNTvaults, trusted contacts, and merchant metadata; TransferV3Multi-Input/Output Consolidation Traces: Record why sub-account UTXOs or balances were consolidated and attribute every individual input and output leg;- Merchant-Signed Digital Receipts: Verify merchant DID signatures automatically while running strict Unicode
NFKCand bidirectional (BiDi) control-character sanitization so spoofed strings can never disguise amounts or payee names; - Peer-to-Peer Encrypted Shared Memos via DID Inbox: Senders can attach an end-to-end encrypted payment memo to a recipient's DID Inbox. The kernel verifies that the envelope sender matches the on-chain sender (
envelope.senderDid === tx.from). Memos from known contacts decrypt and index automatically, while memos from unknown senders land in a quarantinedPENDINGstate—working hand-in-hand with the Account Security Guard inbox so accepting a transfer promotes the memo and burning spam airdrops discards it.
Finally, whenever you activate the Private Overlay in the block explorer, the kernel uses K_seal to render a deterministic Personal Security Seal (PersonalSecuritySeal, with a unique verification code, badge glyph, and hue)—confirming at a glance that the annotations on screen come from your authentic sovereign ledger rather than a phishing site.
4. Closing: From On-Chain Verifiability to End-to-End Isomorphic Verifiability
Stepping back, the architectural thread connecting these layers is straightforward.
First-generation blockchains poured all of their cryptographic rigor into server-to-server consensus while leaving the "last mile" closest to humans and AI agents in the stone age: blindly trusting remote RPC JSON, storing local state in unverified cache tables, and stripping away the business context required for real-world accounting.
By embedding the exact same Verifiable Ledger Core into the blockchain, into every ARC, and into every human and AI agent wallet:
- Outward, the wallet becomes a Light Verification Node that pre-computes expected state, verifies signed checkpoints and deterministic execution receipts, and turns a million endpoints into a distributed audit network that no single gateway can deceive;
- Inward, the wallet replaces fragile local cache tables with an isomorphic append-only event log, Incremental Merkle Trees, and 100% rebuildable AFS projections, while enforcing strict 4-category isolation so secret keys never touch the ledger;
- Upward, the sovereign encrypted annotation ledger (
ocap.annotation.v1) combines zero-knowledge HMAC blind indexing with Passkey PRF and QR session grants to give cold on-chain hashes private, human-readable accounting context.
With every ARC and every wallet ready to verify signed Checkpoint commitments in sub-millisecond time, how does the chain itself deliver 10ms–50ms execution receipts while preserving Byzantine fault tolerance and separation of powers through a HotStuff-Lite core cluster? In the third article of Batch 1, we open up the Verifiable Single Sequencer and Two-Tier Finality architecture.