Embedded Like SQLite, Verifiable Like a Blockchain: Blockchain, Verifiable Ledger, and the Verifiable Ledger Core Inside Every ARC
For well over a decade, software engineering has treated data verifiability as a binary, all-or-nothing choice.
When an application simply needs fast local reads and writes, engineers reach for SQLite or PostgreSQL. It is fast, zero-configuration, and starts inside the process—yet it offers zero cryptographic protection against historical tampering. Anyone who obtains write access to the database—an administrator, a compromised background service, or a runaway AI agent—can silently rewrite past amounts, timestamps, or authorization scopes without leaving a mathematical trace.
Conversely, when a system needs tamper-evident audit trails and multi-party reconciliation, conventional wisdom tells you to "put it on a blockchain." That usually means either pushing business data onto a public chain—paying unpredictable gas fees, waiting on public mempools, and exposing operational metadata—or standing up a multi-node consortium cluster before writing a single line of application logic.
As we evolved the ArcBlock platform and ARC (Agentic Realm Computer), we kept asking ourselves a foundational question: Why can't "embedded like SQLite" and "mathematically verifiable like a blockchain" be the exact same thing?
They can—and they should be—once we decouple the essence of a ledger from the heavyweight machinery of a multi-node public network.
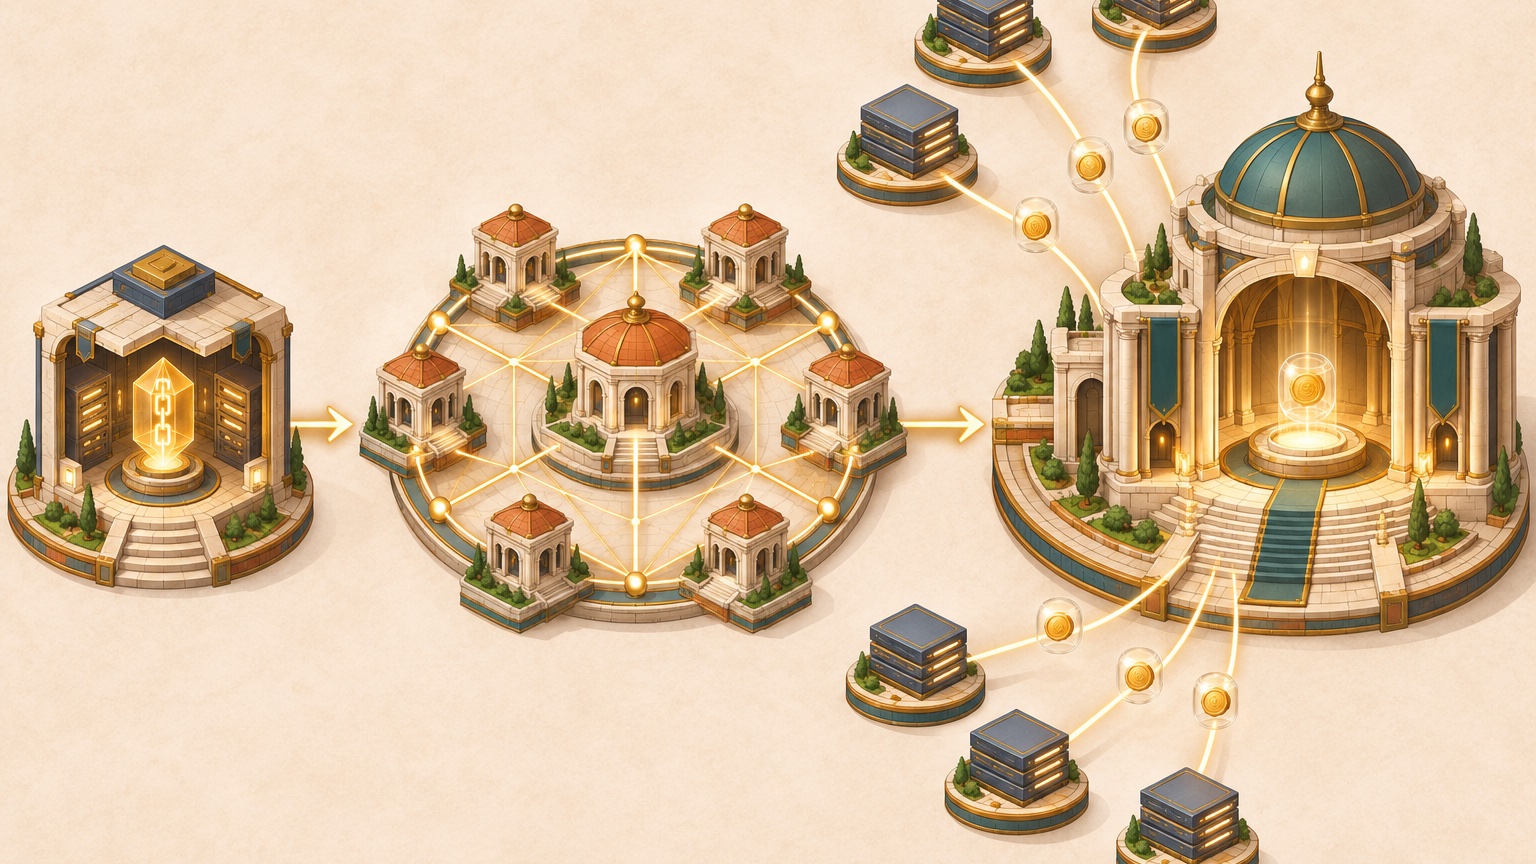
In today's ArcBlock architecture, the Verifiable Ledger Core embedded inside every ARC, the standalone sovereign Verifiable Ledger, and the cross-organization blockchain network (ArcBlock Chain) are no longer three separate systems. They are three concentric rings grown from the exact same cryptographic kernel at different scales of deployment.
1. First Principles: A Blockchain Is a Verifiable Log, Not a Heavyweight Node Cluster
If you strip away peer-to-peer gossip, proof-of-work mining, token inflation schedules, and general-purpose virtual machines from Bitcoin, Ethereum, and modern distributed ledgers, what remains at the very center?
An append-only, digitally signed, hash-chained, and Merkle-committed verifiable log.
Our architecture rests on a simple invariant:
Consensus(Ledger) + Determinism(Algorithm) = Consensus(State)The authenticity of each transaction or event is already guaranteed by the initiator's digital signature (Ed25519, Passkey P-256, or post-quantum ML-DSA). And so long as the state transition algorithm is deterministic, anyone replaying the same sequence of ledger entries on any machine will derive the exact same byte-for-byte state (State = f(Ledger)). The only thing the ledger itself must lock down is the historical ordering of events and a cryptographic commitment to that order.
Seeing this clearly changes the architectural boundaries immediately:
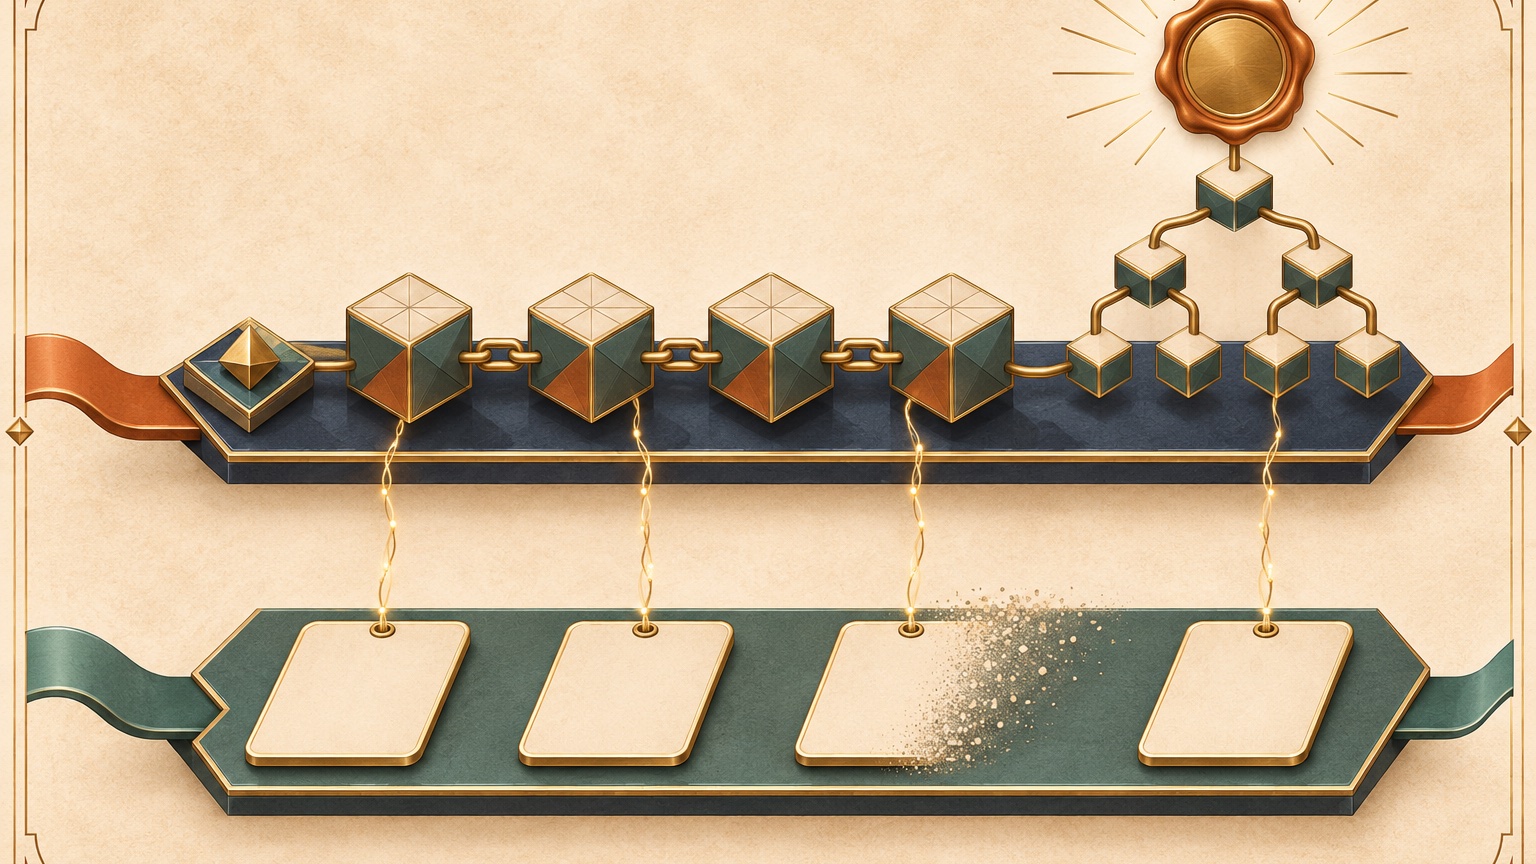
- Verifiability does not require a multi-node network. Even inside a single machine, a single process, an isolated AI agent container, or an offline mobile wallet, as long as events are appended along a cryptographic hash chain and sealed periodically into signed Incremental Merkle Tree checkpoints, that local history is self-authenticating and tamper-evident.
- Distributed consensus and external anchoring are composable layers you add as needed. When a ledger runs inside a single ARC, the instance signs its own checkpoints. When it expands to multi-party collaboration, independent witnesses cosign those checkpoints. When it requires public, cross-organizational finality, it anchors a compact checkpoint digest—under 100 bytes—onto the public mainchain.
Instead of bolting a rudimentary "audit table" onto ARC, we extracted a zero-external-consensus, purely deterministic Verifiable Ledger Core from our blockchain engine and embedded it as standard infrastructure inside every ARC instance.
2. Inside the Verifiable Ledger Core of Every ARC
In the ARC runtime architecture, the Agentic File System (AFS) is the universal abstraction for state and capability. The vledger:// scheme is a core security provider built natively into every ARC.
Whether an ARC instance is running on a developer's MacBook via the CLI (backed by local SQLite), deployed on an enterprise server, or executing at the edge inside Cloudflare Workers (backed by Durable Objects SQLite or D1), it mounts and drives a complete Verifiable Ledger Core locally without needing an external blockchain RPC connection.
1. Hash Chains, Incremental Merkle Trees, and Signed Checkpoints
Whenever an application, workflow, or AI agent inside ARC executes a critical operation—such as a permission change, a budget deduction, a credential issuance, or an external tool invocation—EmbeddedLedger commits the event through a strict deterministic pipeline:
Event Input (from, type, payload, nonce, timestamp)
  │
  ├─► 1. Canonical Serialization (deterministic key ordering → txRaw / txHash)
  ├─► 2. Hash Chain Linking: sha256(prevHash : sequence : msg)
  ├─► 3. Deterministic Entry Hash: computeEntryHash(sequence, txRaw, stateCommitHash)
  └─► 4. Window Sealing (e.g., every 100 entries):
IncrementalMerkleTree → txRoot + stateRoot → Signed Checkpoint- Deterministic Entry Hash (
entryHash): Every entry written to the ledger binds its monotonicsequence, canonical payloadtxRaw, and post-execution deterministic state commitmentstateCommitHash. Modifying a single historical payload, execution outcome, or sequence position breaks the entire downstream hash chain. - Incremental Merkle Tree and Signed
Checkpoint: At configurable window boundaries (for example, every 100 entries or on a timer), the core builds an Incremental Merkle Tree over the window, producing a transaction root (txRoot), a state root (stateRoot), and a link toprevCheckpointHash, sealed with the proposer's cryptographic signature. - Sub-Millisecond Inclusion Proofs: Proving that an event exists inside a signed historical window never requires a full-table scan. Using cached window trees and single-flight proof construction, generating a Merkle inclusion proof takes roughly
1.7ms, while verifying that proof on a client or peer takes just0.03ms–0.08ms.
2. Separating Fact from Content: How an Append-Only Ledger Respects Privacy and Erasure
One of the most common reasons engineering teams hesitate to adopt an append-only ledger in production business systems is privacy compliance—such as GDPR's Right to Erasure. If ledger records can never be modified or deleted, what happens when a record contains personal names, email addresses, or confidential business documents?
From day one, Verifiable Ledger Core enforces a strict architectural separation between Fact (immutable cryptographic evidence) and Content (erasable state payload):
| Record Class | Written to Ledger (Immutable Layer) | Written to State (Updatable / Erasable Layer) | Verification After Erasure or Redaction |
|---|---|---|---|
| Fact-Only Events (transfers, quota deductions, votes, permission toggles) | Full event record (from / to / amount / action is the atomic system fact and contains no raw PII) | Derived current balances, quotas, or permission views | Facts remain permanently auditable; state can be 100% reconstructed by replaying the ledger at any time |
| Fact + Content Events (DID documents, private credential claims, business invoices) | Only the fact skeleton + cryptographic hash (e.g., did + timestamp + contentHash) | The full document body (supports encryption, updates, or physical erasure for compliance) | While content exists, hash(content) == contentHash proves integrity; after compliant erasure, the hash chain and sealed checkpoints remain 100% intact and verifiable |
In short, "append-only ledger" does not mean "unerasable personal text." When a user exercises their right to erasure, the system deletes the document body from the state layer. The contentHash on the ledger reveals zero personal information, yet continues to prove mathematically that the registration occurred at that exact timestamp and that no surrounding ledger pages were altered after the fact.
3. Native AFS Mounts and Verifiable Budget Gates for AI Agents
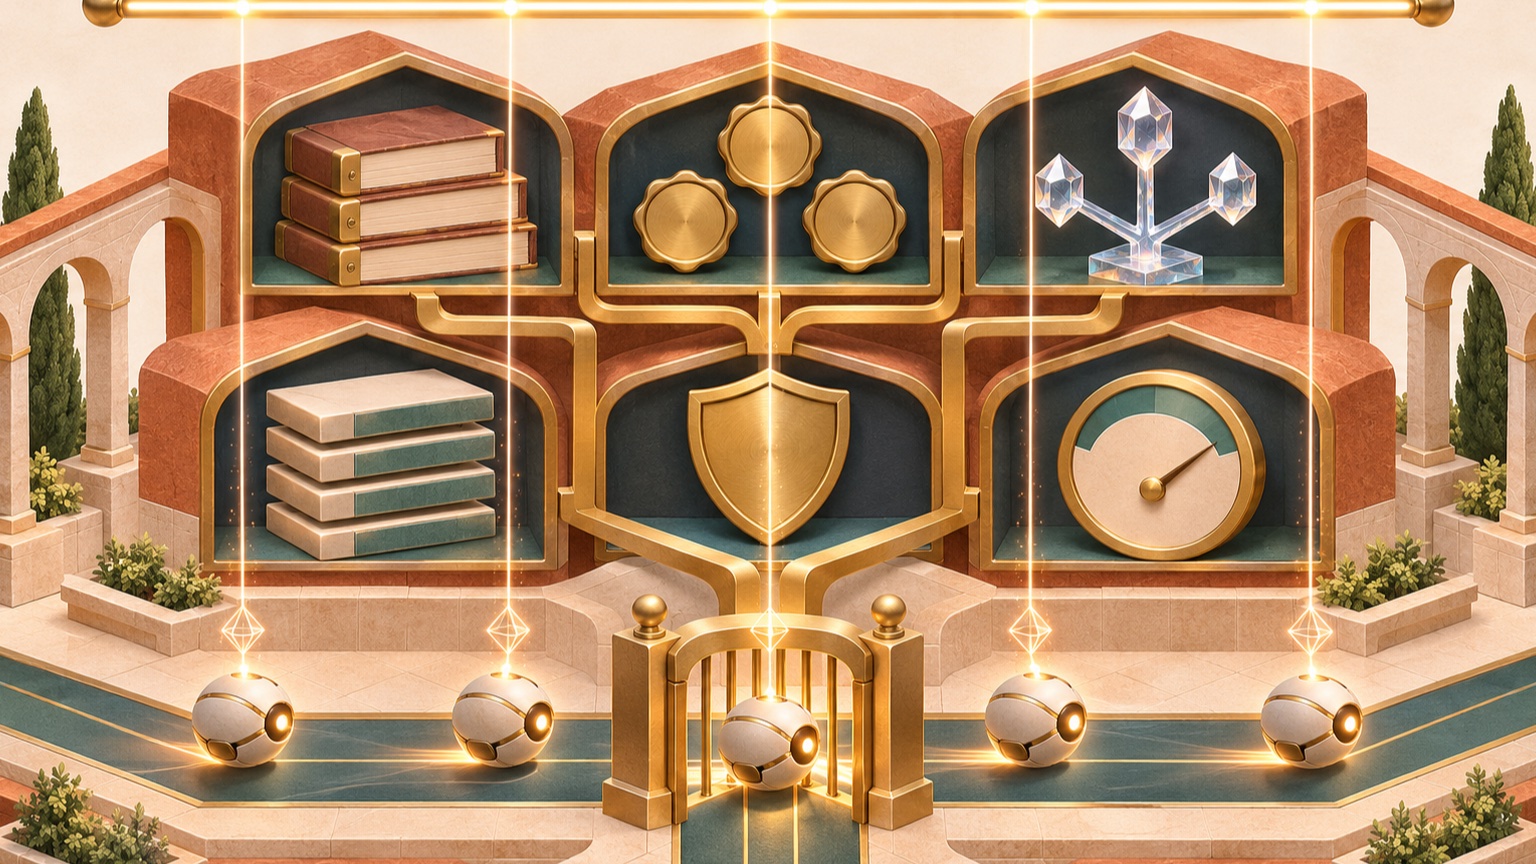
Because Verifiable Ledger Core mounts directly into ARC's file system tree via vledger://, any authorized module or AI agent can read, write, and verify the ledger through standard AFS paths without learning a specialized blockchain SDK:
/entriesand/checkpoints: Read ordered, tamper-evident event streams and signed checkpoint seals;/proofsand/segments: Fetch Merkle inclusion proofs by sequence number, or export compressed cold segments for archival storage;/policyand/consumption: Drive the built-in spending policy and quota metering engine.
Consider a scenario that every organization deploying autonomous AI agents faces today: you run 50 specialized agents across code review, customer support, external API procurement, and cloud provisioning. At the end of the month, your cloud and API spend is 50% over budget. When agent activity lives in ordinary application logs, reconstructing which agent exceeded which delegated scope requires days of forensic log correlation.
Inside an ARC powered by Verifiable Ledger Core, each agent's per-call cap, daily/monthly budget quota, and delegation scope are enforced through /policy, while every consumption event is appended as a signed, verifiable fact under /consumption and sealed into Merkle checkpoints. Compliance auditing and spend attribution stop being forensic fire drills and become sub-millisecond verifiable queries.
3. From Embedded Kernel to Sovereign Verifiable Ledger
When we zoom out from a single ARC process to an entire application, an enterprise department, or a fleet of collaborating AI agents, the same Verifiable Ledger Core scales into its second concentric ring: a standalone sovereign Verifiable Ledger (VLedger).
At the engine level, our runtime natively supports Dual Operating Modes: public backbone Chain Mode and lightweight sovereign Ledger Mode.
For the vast majority of enterprise audit trails, inter-departmental settlements, supply-chain state machines, and dedicated application backends, launching a gas token or recruiting anonymous external miners makes no engineering sense. Running in Ledger Mode gives teams three decisive operational advantages:
- Tokenless Preset with Pure DID Authorization: No token minting or gas-vault ceremony is required. Authorized participants and agents submit verifiable events directly using their DID signatures and delegation certificates.
- Replacing Fragile Master-Slave Database Replication with Kilobyte-Scale Checkpoint Streams:
Traditional high-availability databases rely on complex master-slave replication. Because a Verifiable Ledger guarantees deterministic state derivation (
State = f(Ledger)), every time a checkpoint window seals (e.g., every 100 events), the system streams a compact{ checkpoint, entries }delta—just a few kilobytes—to DID Space, S3, R2, or local NAS. If a server fails, a fresh instance simply replays the ledger segments to deterministically rebuild both theState DBandIndex DBfrom scratch, verifying every signature,txRoot, andstateRootalong the way. Any silent bit-rot or storage tampering in cloud backup is caught immediately during recovery. - Inspired by Modern Banking's "Checkpoint + End-of-Day Reconcile" Discipline:
Modern financial institutions do not run global proof-of-work to manage trillions of dollars in daily clearing. Financial engineering relies on verifiable double-entry logs, periodic checkpoint sealing, automated reconciliation, and deterministic reversal rules when discrepancies surface.
Verifiable Ledgerbrings that battle-tested banking discipline directly into software and agent infrastructure.
4. Growing Into a Network of Verifiable Ledgers: VLedger Anchors and the True Role of the Mainchain
If every ARC, every application, and every enterprise can run its own fast, private, zero-gas Verifiable Ledger, why do we still need the public ArcBlock Chain?
This is where the three concentric rings close the loop: we are not building a monolithic single chain that tries to execute every computation in the world; we are building a Network of Verifiable Ledgers that anchor into and interoperate through a high-trust public settlement backbone.
1. Why Enterprises and AI Agents Need Cross-Tier Checkpoint Anchoring
A Verifiable Ledger running on an enterprise's private servers prevents tampering by external attackers and ordinary insiders. Yet when dealing with external auditors, regulators, or cross-organization counterparties, one ultimate trust question remains: What if the enterprise's own root administrator deletes the entire local ledger database and re-signs a fabricated history from genesis using the server's private key?
The answer is Checkpoint Anchoring.
An embedded ARC ledger or an enterprise Verifiable Ledger can periodically—every hour, every day, or immediately after a high-value contract execution—package its latest checkpoint digest into a minimalist AnchorTx and publish it to an organizational parent ledger or the public ArcBlock Chain:
message AnchorTx {
  bytes  source_id         = 1; // DID of the source Verifiable Ledger
  uint64 checkpoint_height = 2; // Sealed checkpoint height
  bytes  merkle_root       = 3; // 32-byte Merkle Root (covering txRoot and stateRoot)
  uint64 event_count       = 4; // Number of events in the window
  bytes  metadata          = 5; // Optional extension metadata
}
The entire on-chain anchor transaction is under 100 bytes.
2. How VLedger Anchoring Differs Fundamentally from Traditional L2 Rollups
Readers familiar with Ethereum L2 rollups often ask how this compares. The difference lies in data sovereignty and cost structure:
| Dimension | Traditional Blockchain L2 Rollup | ArcBlock VLedger + Checkpoint Anchor |
|---|---|---|
| Data Availability & Residency | Must publish compressed transaction batches to public L1 calldata/blobs or an external public DA layer | 100% of raw business data stays inside the application, enterprise server, or private DID Space—zero public leakage |
| Role of the Mainchain | Stores heavy transaction blobs and verifies or re-executes state transitions | Acts strictly as an unforgeable external timestamp notary and state continuity anchor |
| On-Chain Cost & Throughput Ceiling | Bounded by public DA bandwidth and L1 block space pricing | Minimal (< 100 bytes per anchor); local ledger throughput is completely unconstrained by the mainchain |
| Audit & Counterparty Verification | Entire transaction history is publicly exposed on-chain | Selective Disclosure: present only the relevant local entry and its Merkle inclusion proof to an authorized auditor or counterparty, verified against the public mainchain anchor |
Once a checkpoint hash is anchored onto the mainchain, even a root administrator with full physical access to the private server can never silently rewrite or roll back a single local record prior to that checkpoint. The public anchor acts as an immutable cryptographic wax seal on the global timeline.
5. Closing: Anyone Can Verify. Nobody Has To.
Stepping back to look at all three concentric rings together:
- At the innermost ring,
Verifiable Ledger Coresits quietly inside every ARC and every terminal wallet like SQLite—adding zero network overhead while sealing every local state change and AI agent budget consumption into a hash chain and Incremental Merkle commitment. - At the middle ring,
Verifiable Ledgerlets any application or organization run a sovereign, tokenless verifiable state machine with kilobyte-scale deterministic backup and banking-grade reconciliation. - At the outermost ring,
ArcBlock Chainserves as the public settlement and anchoring backbone, weaving thousands of independentVerifiable Ledgersinto a cross-organizational web of verifiable trust using anchors smaller than 100 bytes.
There is a guiding principle from our architecture notes that captures this philosophy in seven words: "Anyone can verify. Nobody has to."
Freeing verifiable ledgers from heavyweight node dogma—and making them as ubiquitous and embeddable as SQLite and file systems—is why we built Verifiable Ledger Core into every ARC. In the next article of this series, we will follow this exact same kernel into the user's phone and AI agent endpoints to see what happens when the wallet itself becomes a light verification node backed by an isomorphic Verifiable Ledger and a sovereign encrypted annotation ledger.