Transactions and Credentials in One Envelope: Bitmap Revocation, Selective Disclosure, and Encrypted NFTs
For years, blockchain engineers and decentralized identity communities have resembled two departments in the same building speaking different dialects.
Ledger engineers work with transactions: a sender (from), public key (pk), replay-protection sequence (nonce), transaction type (type), application payload (itx), sender signature (signature), and a list of multisignature or delegated endorsements (signatures).
Identity engineers work with Verifiable Credentials (VCs): an issuer, issuance time, credential type, credentialSubject, and cryptographic proof.
When we placed these two structures side by side on a whiteboard, a basic question emerged:
Once we remove their historical naming conventions, do a transaction and a Verifiable Credential share the same underlying cryptographic structure?
That led to a second question: if transactions, credentials, and NFTs share an envelope model, can we combine public verification with private control of the underlying data?
Our work addresses these questions through four designs: a shared VerifiableEnvelope, ArcSpace proof anchoring without storing large payloads on-chain, O(1) bitmap revocation and SD-JWT selective disclosure, and EncryptedAssetEnvelope NFTs with a public exterior and encrypted payload.
1. The structural correspondence between transactions and credentials
Why maintain separate encoders, signature-verification pipelines, and delegation validators for on-chain transactions and off-chain credentials?
Their histories explain much of the separation. Transaction protocols grew out of high-throughput binary state machines that prioritize compact, deterministic bytes. W3C credentials emerged from the semantic-web and JSON-LD tradition, with remote @context resolution and more extensive textual structures.
At the cryptographic level, however, a transfer instruction and a university diploma can use the same basic container:
A DID entity (
issuer) makes a cryptographically signed commitment (signature) to a typed, structured statement (type+payload), within a sequence or validity boundary (nonce/validFrom), optionally accompanied by endorsements and inclusion evidence (proofs).
This observation underlies the VerifiableEnvelope specification we are designing for the next protocol evolution. Its goal is to bring the independently operating transaction and off-chain VC systems onto a shared cryptographic foundation.
A résumé stored as a PDF is still a résumé
A container format should not erase the domain concepts it carries. Our design boundary is explicit: unify the cryptographic envelope and signature-verification pipeline, while retaining Transaction as an instruction requesting a state transition and VerifiableCredential as an issued statement about facts or authority.
A résumé and a property contract can share a PDF renderer and digital-signature verifier. Their common file format does not turn them into the same business object.
| Dimension | Transaction | Verifiable Credential | Shared VerifiableEnvelope |
|---|---|---|---|
| Issuing entity | Sender from | Credential issuer | issuer (DID identifier) + pk |
| Validity and replay protection | Monotonically increasing account sequence / time window | Credential ID / validFrom / validUntil | nonce + optional lifecycle boundaries |
| Payload semantics | State-transition instruction itx | Subject claims in credentialSubject | type + Canonical CBOR payload |
| Cryptographic commitment | Sender signature | Issuer proof | Domain-separated deterministic CBOR signature |
| Endorsements and state evidence | signatures / delegation chain | On-chain inclusion proof / state anchor | Composable proofs[] array |
In this design, once the sequencer executes a transaction and appends a MerkleInclusionProof and CheckpointSignature to proofs[], the transaction can circulate as an independently verifiable offline receipt without another format conversion.
2. ArcSpace and Proof-Only offloading
A common envelope does not require putting identity credentials, long AI reasoning logs, or high-resolution commercial assets into the blockchain's primary state tree.
Replicating large application payloads permanently across every node creates three problems: storage growth and its associated costs, privacy and erasure requirements that conflict with immutable public records, and disclosure of confidential business data.
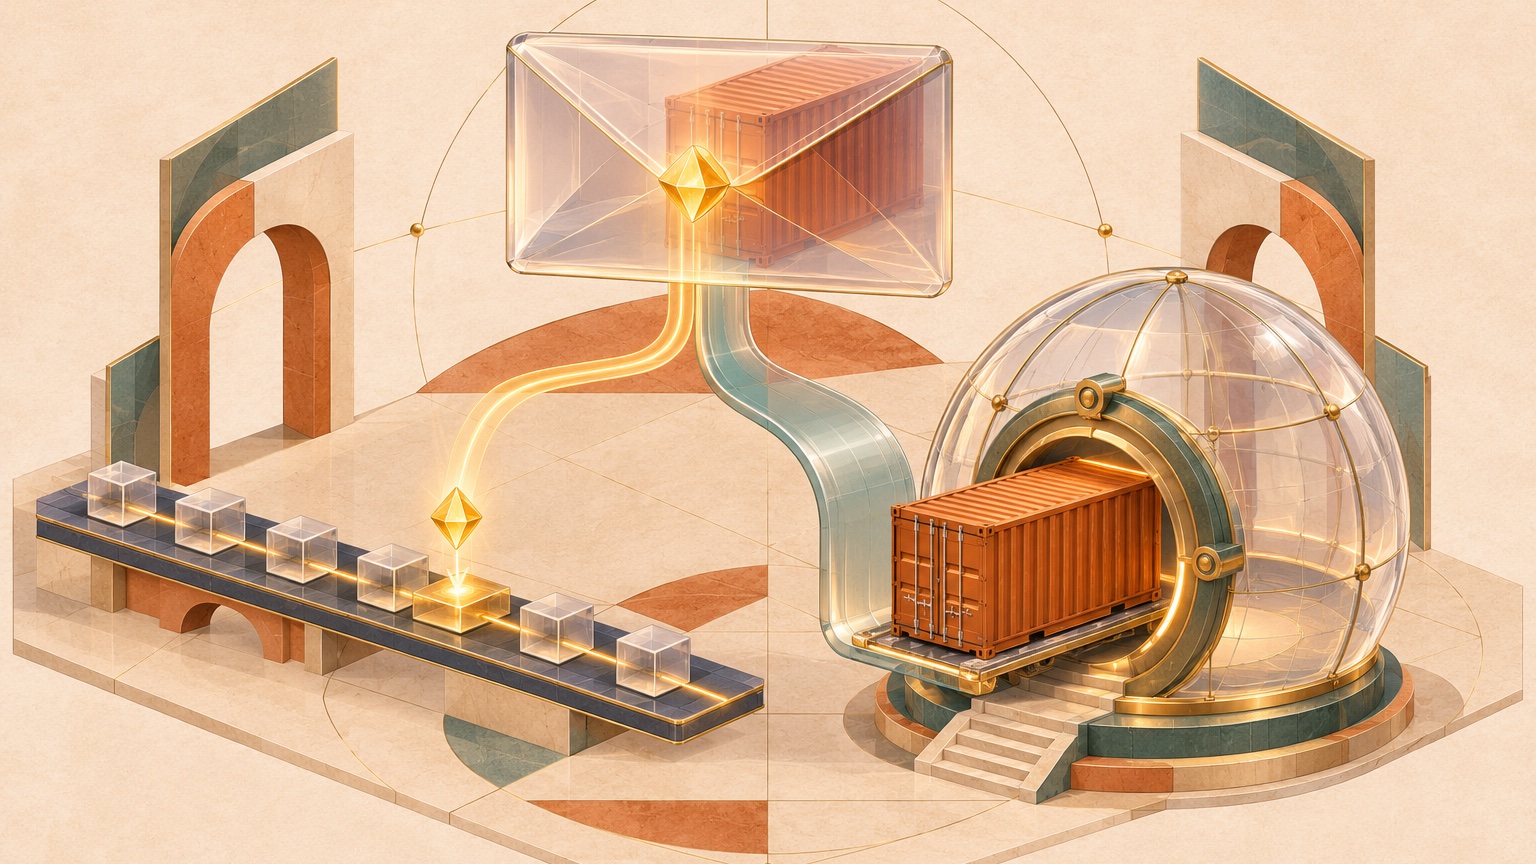
In the implemented @ocap/ledger-core architecture, ArcSpace, the user's sovereign storage space (DID Space), holds large encrypted payloads. The chain follows a Proof-Only approach, recording cryptographic commitments:
- Large payloads remain in
ArcSpace. Full credentials, attachments, NFT media, and encrypted data packages reside in the user's storage, where access control and compliant erasure can be applied. - The chain records fixed-size, 32-byte commitments. The core uses
computeArcSpaceCheckpointRootandcomputeNftPayloadCommitmentDigestto record Merkle roots or payload digests. - No per-byte on-chain storage rent for the offloaded content. Each anchor remains a fixed-size commitment of a few dozen bytes. The chain avoids carrying the large payload itself, keeping the corresponding state compact.
3. O(1) bitmap revocation and SD-JWT selective disclosure
Credential and delegation systems face two difficult operational questions:
- How do you revoke authority? If an employee leaves or an agent's delegated key may be compromised, a verifier needs a fast status check. Querying the issuer for every presentation creates a phone-home channel that reveals the holder's activity.
- How do you avoid excessive disclosure? A credential may contain ten fields, including a name, date of birth, document number, and qualification level. A verifier that needs only qualification information should not receive the other private fields.
In @arcblock/vc and the ledger core, we address these with two standardized primitives.
W3C BitstringStatusList: over 130,000 statuses in a 16 KB bitmap
Following the W3C BitstringStatusList v1.0 standard and the compact-revocation-list approach, each credential maps to a position (statusListIndex) in a dense bitstring:
- 1-bit mode.
0indicates valid;1indicates permanently revoked. - 2-bit mode.
00indicates valid,01permanently revoked,10temporarily suspended and recoverable, and11reserved. - Compact storage and
O(1)lookup. In 1-bit mode,131,072credential statuses occupy only 16 KB before compression. Gzip compression and Multibase encoding can reduce sparsely revoked lists to a few hundred bytes.
The verifyPresentation pipeline in @arcblock/vc accepts an injected RevocationChecker. A verifier fetches and caches the issuer-signed status list, then checks a credential's revocation or suspension through constant-time O(1) bit operations. There is no large per-credential blacklist to scan, and no need to notify the issuer of each presentation's participants and timing.
SD-JWT selective disclosure and holder key binding
To avoid revealing every claim in a presentation, we support SD-JWT (Selective Disclosure JWT) using salted hash commitments.
At issuance, each selectively disclosable attribute is represented by a randomly salted disclosure, [salt, claimName, claimValue]. Its SHA-256 digest goes into the _sd array covered by the issuer's signature, rather than exposing the attribute in plaintext.
When a user or agent presents the credential, it supplies only the disclosures needed for that interaction. It also signs a kb-jwt (Holder Key Binding JWT) with its DID key, binding the presentation to the verifier's current nonce and aud. The verifier checks that the disclosed claims match the issuer's commitments while undisclosed claims remain hidden. Key binding protects against reuse of an intercepted presentation in another verification context.
4. EncryptedAssetEnvelope: a public NFT with a private payload
A practical test of envelopes and proof offloading is the tokenization of paid digital content, commercial software licenses, private AI model weights, or confidential contracts.
Conventional NFTs leave an awkward choice. Put the underlying content at a public tokenURI, such as a public IPFS link, and anyone can download it without holding the NFT. Put it behind a project-controlled database and NFT-gated login, and access depends on that server remaining available.
The requirement is more precise: an asset should be publicly discoverable, verifiable, and transferable, while its encrypted payload is delivered to its authorized owner without a centralized plaintext-custody server.
In @ocap/ledger-core, we designed and implemented ocap.nft.encrypted.v1 (EncryptedAssetEnvelope) as a two-layer protocol structure.
The public discovery header
Public metadata and cryptographic anchors allow explorers, marketplaces, and prospective recipients to inspect the asset without seeing its private contents:
- Display fields:
title,summary,previewUri, andcontentType. plaintextHash. A SHA-256 commitment to the original plaintext payload, enabling the recipient to check the decrypted content against the committed bytes.cekCommitmentHash. A hash commitment to the content-encryption key (CEK), used to detect key substitution during transfer.arcSpaceUri. A URI identifying the ciphertext stored inArcSpace.
The encrypted inner payload
The content is sealed with AES-256-GCM, with authenticated additional data bound as AAD = assetAddress || issuerDid || plaintextHash. The CEK is wrapped for the current owner using secp256k1-ECDH-HKDF-SHA256:
- Seal for the owner (
sealEncryptedNftForOwner). The creator generates a randomCEKand encrypts the content. ECDH with the owner's public key derives the shared key used to wrap the CEK asencryptedCek, which the owner's private key can unwrap. - Open locally (
openEncryptedNftAsOwner). In a local wallet or ARC runtime, the owner uses its private key to recover theCEK, checkscekCommitmentHashand theAES-256-GCMauthentication tag, decrypts the content, and verifiesplaintextHash. Neither plaintext nor keys pass through a third-party server.
Zero-copy key rewrapping at handover
Suppose Alice transfers an encrypted NFT containing a 500 MB professional dataset or paid media file to Bob. Must she download, decrypt, re-encrypt, and upload the entire file?
The rewrapEncryptedNftForNewOwner primitive avoids that bulk operation:
- The 500 MB ciphertext remains in
ArcSpace. The existingCEKcan remain unchanged, with a key-rotation path available when stronger separation between ownership periods is required. - Alice locally unwraps the 32-byte
CEK, then uses Bob's public key to create a new ECDH-wrappedencryptedCek. The handover includes ahandoverSignatureand a monotonically increasinghandoverIndex. - The on-chain state transition atomically transfers both NFT ownership and the pointer to the updated
EncryptedAssetEnvelopeto Bob.
A payload hundreds of megabytes in size can therefore change its authorized key recipient through a small cryptographic rewrapping operation, without moving the bulk ciphertext.
Public verification and private control belong together
Platform applications offer private data access and responsive interactions, but their credentials and assets often depend on a platform-controlled database. Conventional public chains offer tamper-evident verification while exposing data to every observer.
The VerifiableEnvelope unification layer remains under development. The implemented mechanisms in the core and credential stack take complementary steps: ArcSpace Proof-Only offloading, BitstringStatusList revocation, SD-JWT selective disclosure, and the two-layer EncryptedAssetEnvelope. Together, they show how public verification and user-controlled private data can coexist in the same architecture.
The chain keeps verifiable commitments. The owner controls the encrypted content. That division gives credentials and assets a practical foundation for interactions among people and AI agents.